North Korean Hackers Staged Fake Job Interviews to Infiltrate Binance in Massive $6.3B Crypto Heist
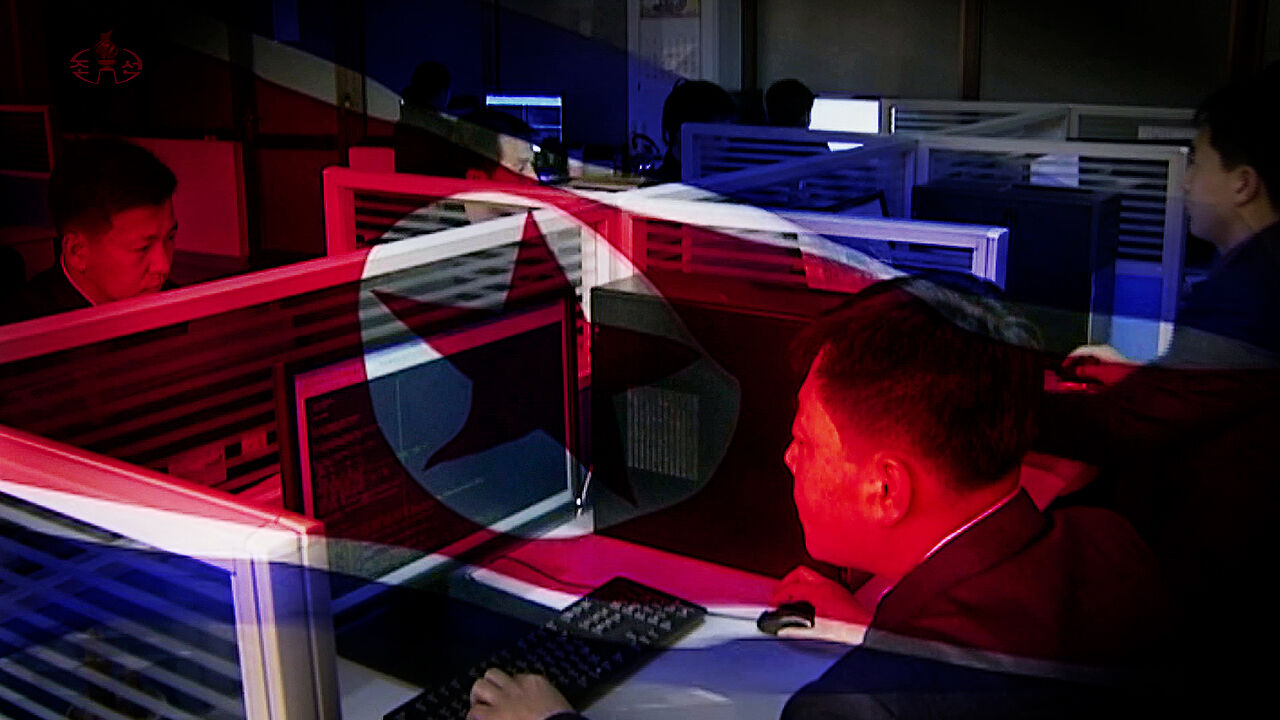
Key Points
- North Korean hackers spent five months targeting Binance employees, staging fake executive job interviews and malware-laced assignments to steal $6.34 billion in crypto.
- The breach has sparked urgent alarms in South Korea after security researchers warned domestic exchanges could be the next target for the elite cyber unit.
- Binance managed to freeze 3.8 trillion won of stolen assets and covered 98% of user losses, while US analytics firm TRM Labs identified the group as the notorious 'TraderTraitor' unit.
Summary A jaw-dropping cyber heist against Binance, the world's largest cryptocurrency exchange, has revealed the astonishing lengths to which North Korean state-sponsored hackers will go. According to an investigative report released by Binance, North Korean cyber operatives conducted a meticulous, five-month social engineering campaign—complete with fake corporate recruitment and mock executive interviews—to siphon off approximately 63.4 billion dollars (8.4 trillion Korean won) in digital assets.
The breach began in June when operatives duped a Binance engineer into downloading malicious software disguised as legitimate work files. This initial intrusion compromised internal personnel records, specifically exposing staff handling cryptocurrency wallet security and authentication. Three months later, hackers shifted tactics to job platforms, contacting another company engineer with an enticing career offer. Posing as a chief executive officer during a staged video job interview, the attackers instructed the candidate to complete an evaluation assignment that delivered a second payload of malware. This gave hackers the administrative keys required to manipulate company systems directly.
The grand theft unfolded with lightning speed in late October. In a mere four minutes, the group liquidated and transferred more than 230 million Ripple tokens, quickly following up with major drains of Solana, Bitcoin, and Ethereum. Binance reported that while approximately 3.8 trillion won worth of assets was quickly frozen or intercepted, the exchange covered more than 98% of overall losses using internal corporate reserves and secure insurance funds.
Blockchain analytics firm TRM Labs attributed the operation to 'TraderTraitor,' an elite North Korean hacking unit notorious for executing high-yield crypto robberies to evade international sanctions. Security analysts in Seoul and abroad emphasize that as South Korea remains one of the world's most active cryptocurrency trading hubs, domestic exchanges and tech professionals must brace for similar spear-phishing and interview impersonation schemes. The incident underscores how modern cyber warfare increasingly exploits human ambition and professional networking platforms rather than relying solely on technical software exploits.
Sponsored · Ad