'Dozens of Laptops in the Living Room': U.S. Busted Secret 'Laptop Farms' Fueling North Korean Infiltration
Key Points
- The FBI and federal prosecutors in Texas raided over 40 residences in 'Operation Lone Star Roundup,' seizing 187 laptops and peripherals used by North Korean IT workers to illegally work for U.S. comp
- The sophisticated operation, tracked by cybersecurity analysts as 'Famous Chollima,' funneled corporate salaries directly into North Korea's weapons and nuclear development programs.
- North Korean operatives used stolen identities and VPNs while relying on domestic U.S. accomplices to run living-room laptop hubs, generating an estimated $800 million in illicit foreign currency in 2
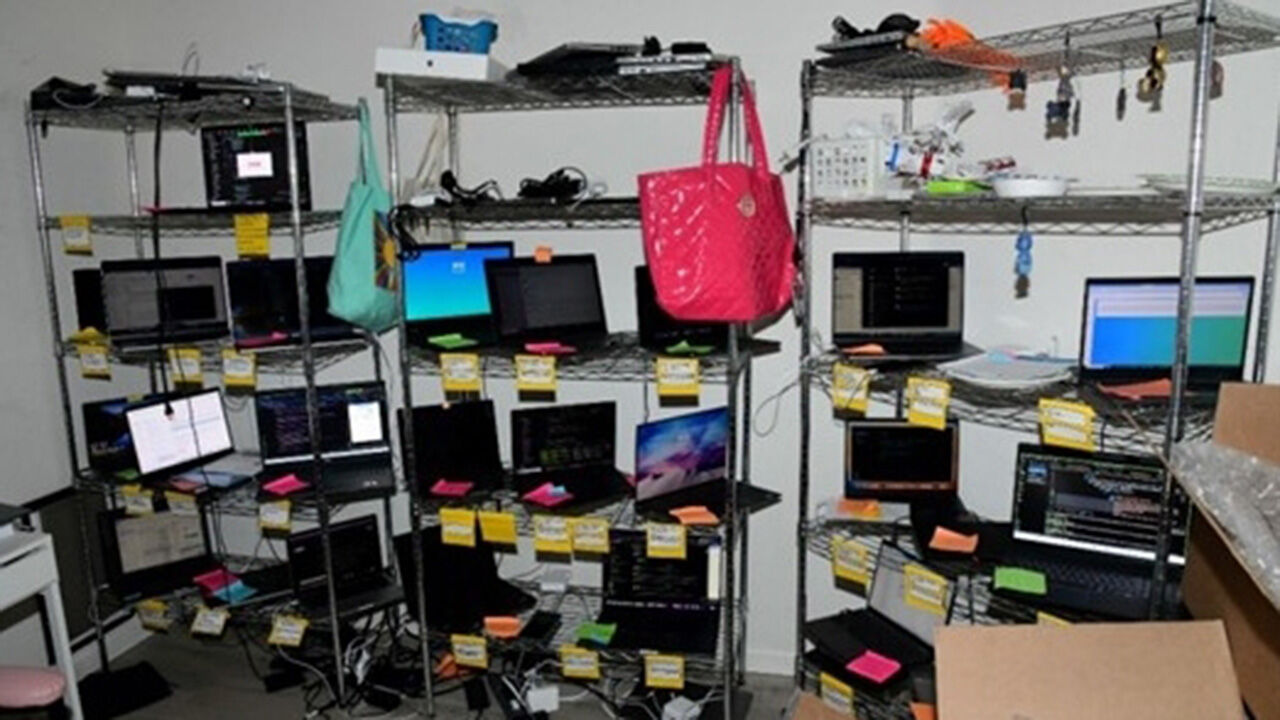
Summary A sprawling international cyber scheme involving North Korean IT operatives and covert "laptop farms" across the United States has once again been dismantled by federal authorities. The Federal Bureau of Investigation (FBI) and the U.S. Attorney's Office for the Northern District of Texas executed a statewide sweep dubbed "Operation Lone Star Roundup," raiding over 40 residential locations and seizing 187 laptops, keyboards, video displays, and mouse devices used to illicitly funnel remote corporate access to North Korean workers.
According to investigators, the scheme exploited the widespread adoption of remote work. North Korean tech workers secured high-paying IT jobs at U.S. firms by using stolen or forged American identities paired with virtual private networks (VPNs) to fake domestic locations. To maintain the illusion of being local employees, they relied on domestic U.S. facilitators who hosted dozens of employer-issued laptops in private living rooms and apartments. These facilitators installed remote desktop software, maintained the hardware setups, and laundered corporate paychecks directly back to state-controlled North Korean bank accounts.
U.S. cybersecurity firm CrowdStrike has tracked this syndicate and its network of co-conspirators under the designation "Famous Chollima." Officials highlighted that these operations represent far more than ordinary employment fraud. Joseph Rothrock, Special Agent in Charge of the FBI Dallas Field Office, stressed that the illicit network directly financed North Korea's weapons of mass destruction, ballistic missile, intelligence, and nuclear programs. Each seized laptop represented a compromised company unwittingly paying a North Korean operative.
Federal prosecutors warned that domestic accomplices claiming ignorance would face severe legal consequences. Ryan Raybould, an assistant U.S. attorney, pointed out the absurdity of having dozens of running laptops stacked in a residential living room while asserting zero knowledge of illicit activity. The illicit revenue generated by such operations is staggering; U.S. Treasury estimates cited by local media suggest North Korean IT workers generated approximately $800 million (around 1.08 trillion Korean won) in 2024 alone through similar schemes. Crackdowns remain ongoing, following earlier multi-state busts and an 8.5-year federal prison sentence handed to an Arizona facilitator convicted in 2023.
Sponsored · Ad